PDC:Primary Domain Controller,ADC:
Primary Domain Controller: A service in a Windows server that manages security for its local domain. Every domain has one PDC, which contains a database of usernames, passwords and permissions.
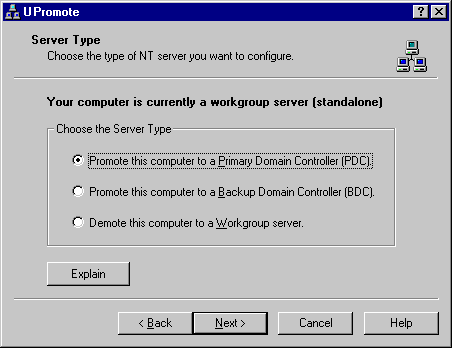
Primary Domain Controller is a Microsoft Windows NT domain controller that contains the master copy of the Security Account Manager (SAM) database.
To configure time synchronization via Group Policy:
Open Group Policy Management Console
Create a new GPO
Open the GPO and navigate to Computer Settings -> Administrative Templates -> System -> Windows Time Service -> Time Providers
Double click the Configure Windows NTP Client.
Set the state to Enabled
Configure the Typeto NTP
Configure NTPServerto point to an IP address of a time server, followed by ,0x8, for example: 131.107.13.100,0x8
Close the Group Policy Editor
In the Security Filteringpane of the Group Policy management console remove Authenticated users for the newly created policy and add the machine that holds the PDC Emulatorrole
Link the GPO to Domain ControllersOU
How To Troubleshoot
To see current configuration of the Windows Time service, use the following command in an elevated command prompt:
w32tm /query /configuration
to see the current source for time synchronization use the following command:
w32tm /query /source
BDC is a Backup Domain Controller
A primary domain controller (PDC) is a server used in computer networks for managing users and groups on a particular segment of a local area network (LAN). The server stores user information and access permissions for network resources, such as other computers or printers, throughout the network. The PDC then provides a single access point for users to log-on to the network and gain access to its resources, thereby alleviating multiple user-name and password combinations.
Delegation of control is when an organizational unit (OU) — an object or group in a computer directory — is given a certain amount of control over functions. The control is usually minimal compared to the task, so the user can only perform the specified task and nothing else. Administrators and people in high positions, such as managers and owners, are given the highest delegation of control, with few restrictions on actions. The control is usually split into departments, giving managers control of a single OU that allows the manager to add or delete users.
An OU is a directory of users and serves several purposes. It allows redundant data, such as two people with the same name but in different departments. This also gives users a way to organize employees and other users in terms of department, employee level and overall delegation of control.
Under the Domain Name System (DNS) which is used to allow people to type in words rather than numeric web addresses to reach a particular website, a top level domain is the last part of a domain name, after the final dot. Here at wiseGEEK, for example, the top level domain is “com.” Top level domains fall into a number of different categories, depending on who is allowed to use them.